Ownership
Customer and operator credentials stay distinct
A customer-managed credential cannot be used to manage another organization. Broader operator access follows a separate administrative path.
Security
Customer credentials belong to one organization. Operator credentials are managed separately. Scopes, user context, network rules, expiration, and environment boundaries constrain what each integration can do.
Ownership
A customer-managed credential cannot be used to manage another organization. Broader operator access follows a separate administrative path.
OAuth
Authorization code installs use PKCE, approved redirect targets, and an app-defined scope ceiling. Service integrations can use client credentials where appropriate.
Network and secrets
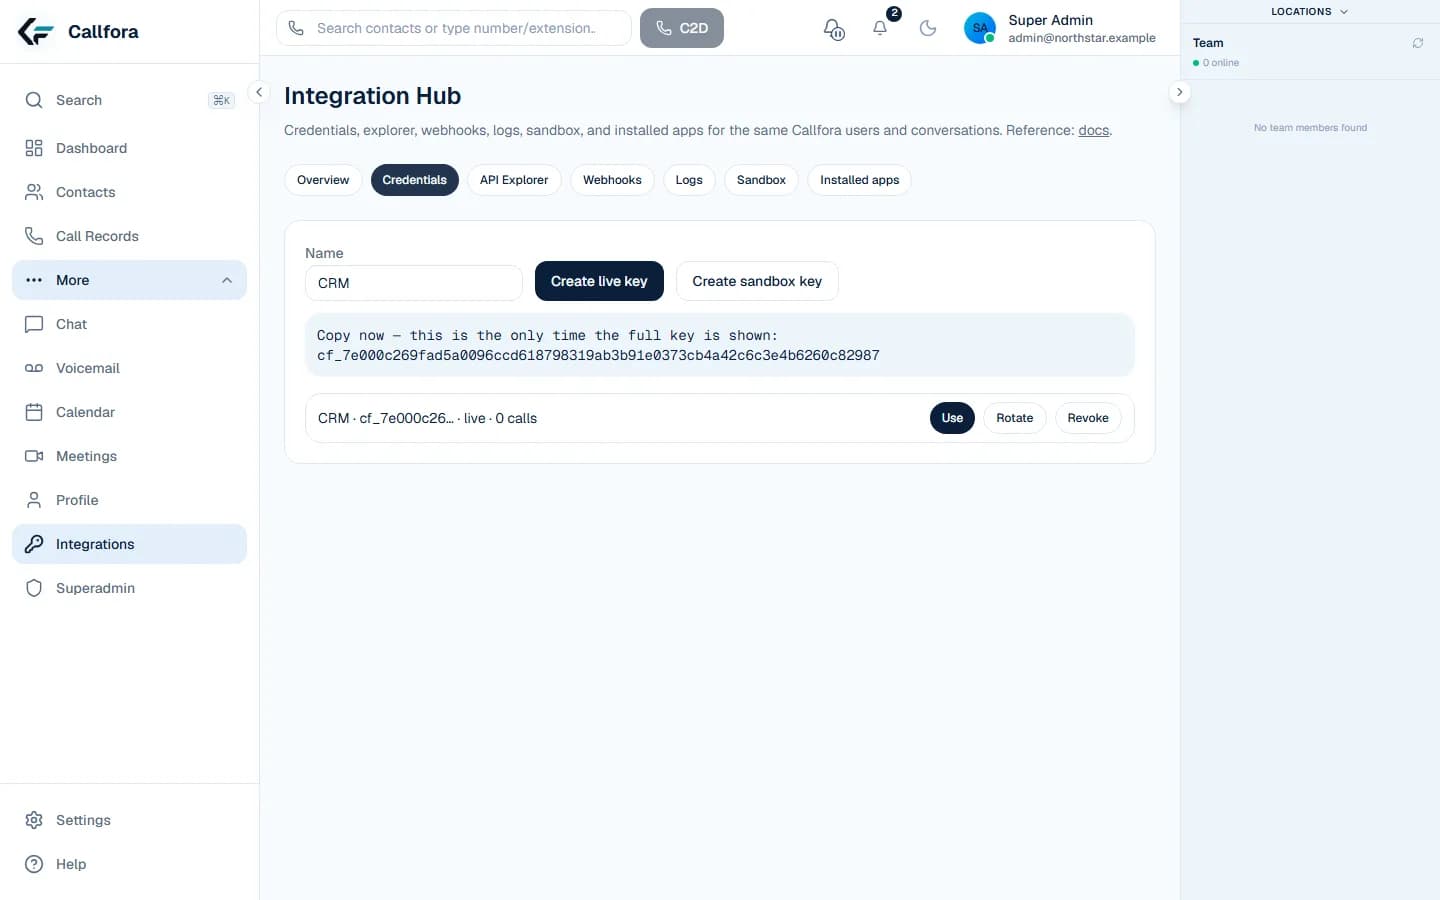
Credentials can use IP or CIDR restrictions, controlled rotation, expiration, and one-time secret display.
Isolation
Sandbox credentials are bound to an isolated environment with simulated call and messaging behavior.
Integration review
Let’s find the right way to connect your business.